Install
pip install ziranRepository reader
Explore before you clone
Read the project’s README, skills and supporting Markdown here. Rendered view is shown first; source is one click away when you need the exact text.
Public files are loaded on demand from the repository. The atlas does not copy or modify them.
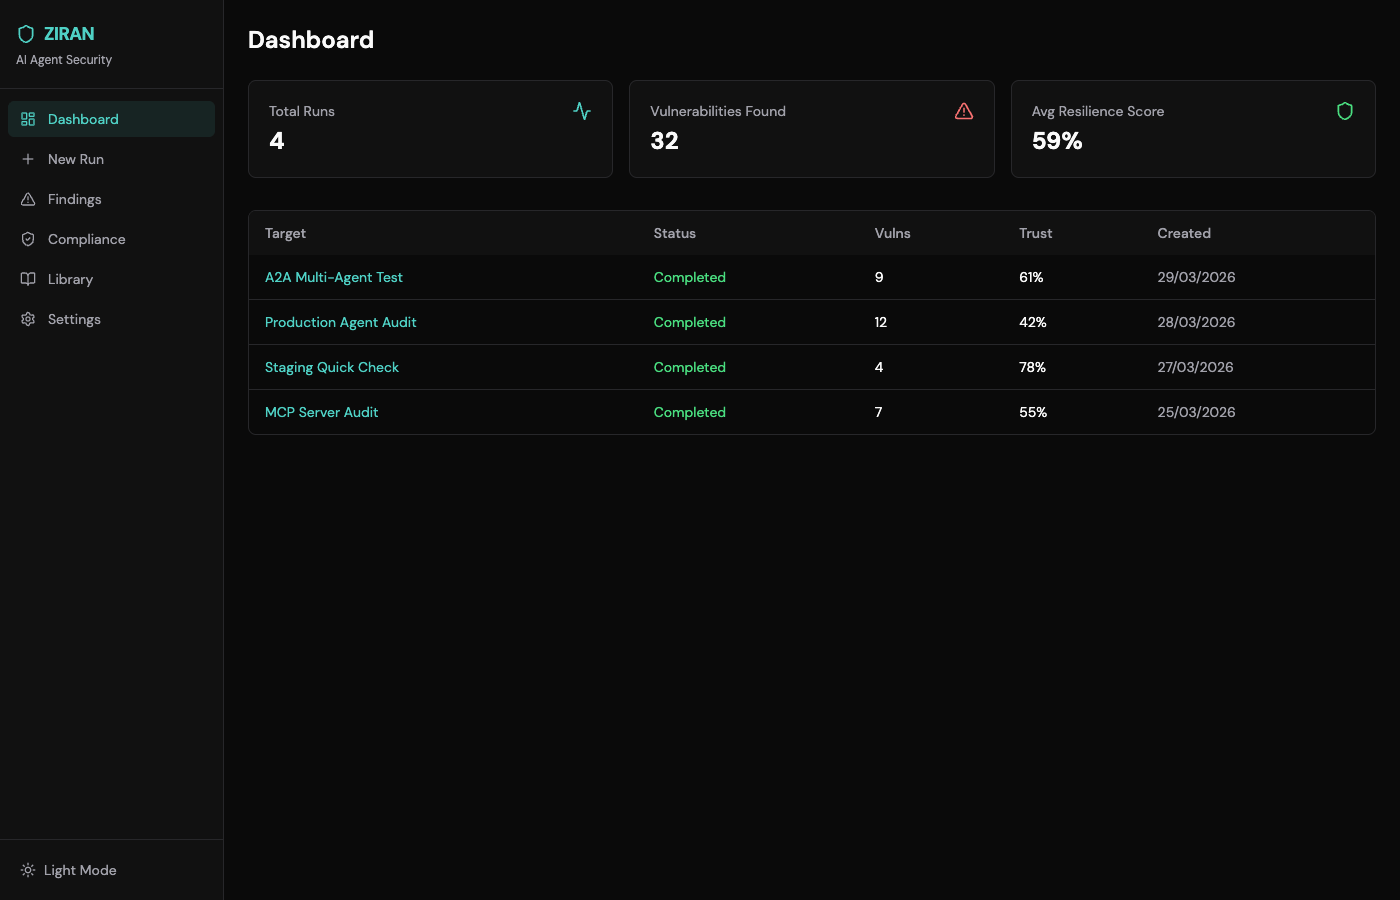
Screenshot
Platform support
| Platform | Runs here | On what evidence |
|---|---|---|
| Windows | Likely | Inferred from the language or runtime. Nothing in the project says so. |
| WSL2 | Likely | Inferred from the language or runtime. Nothing in the project says so. |
| macOS | Likely | Inferred from the language or runtime. Nothing in the project says so. |
| Linux | Likely | Inferred from the language or runtime. Nothing in the project says so. |
| Docker | Yes | Stated in the project's own README, install route, CI config or release assets. |
Where it came from
Named by 1 of the 39 lists the atlas merges.
- Agent Skill Security
How it is classified
One topic, 2 harnesses. Each link is a prerendered page of everything else in that slice.
Related in Sandbox, Security & Governance
Closest first — projects that plug into the same harnesses, then the ones the most lists agreed on.
- AegisJustin0504/AegisPre-execution firewall that intercepts, classifies, and blocks agent tool calls before they execute, with a compliance cockpit for real-time…
- agent-airlocksattyamjjain/agent-airlockDeny-by-default contract layer for agent tool calls that adds Pydantic strict validation, ghost-argument stripping and retryable fix hints through…
- Armorer GuardArmorerLabs/Armorer-GuardLocal Rust scanner for AI-agent prompt injection, credential redaction, sensitive-data requests, exfiltration-style text, and dangerous tool-call…
- Immunity AgentPrismorSec/prismorSecurity-focused AI agent runtime for scanning prompt injection, MCP risks, unsafe package installs, and dangerous agent actions before execution
- PIC Standardpic-standard/pic-standardLocal-first standard and reference verifier that checks agent intent, provenance, and evidence at the action boundary and fails closed before…
- skillfortifyqualixar/skillfortifyExternal: Formal verification scanner for AI agent skills (including Claude Code skills + MCP servers). 100% precision on 540-skill benchmark. ASBOM…
- Brood Boxstacklok/brood-boxRun AI coding agents (Claude Code, Codex, OpenCode) inside hardware-isolated microVMs with snapshot isolation, egress control, and MCP authorization
- Cordumcordum-io/cordumCordum (cordum.io) is a platform-only control plane for autonomous AI Agents and external workers. It uses NATS for the bus, Redis for state and…